Most enterprise AI rollouts fail the same way. A handful of people become fluent and productive with it. Most employees try it once, get an unhelpful answer, and go back to what they were doing. IT sees neither group clearly — only a line item on a vendor invoice that keeps growing.
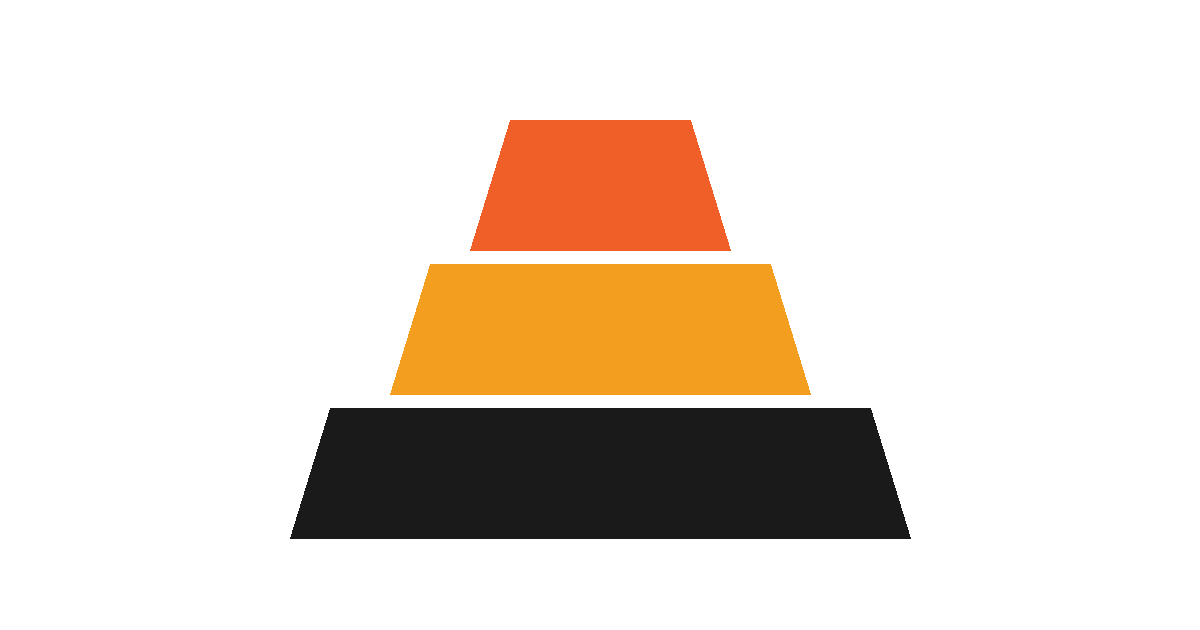
The usual response makes it worse: buy a seat-based licence for everyone, or lock it down to a small approved group. Both ignore the fact that AI usage inside a real organisation is not uniform. It is a pyramid.
The three tiers
Champions, at the top. A small number of people use AI daily and it visibly changes their output. They have proven the value already — the only decision left is which subscription fits them: individual, team or enterprise plan, matched to the work and to company requirements.
Exploring users, in the middle. Value is real but not yet proven for this group. They get a controlled allowance: a choice of models through supported tools, routed through a shared model controller so usage stays inside policy without blocking experimentation.
Occasional users, at the base. Some use still belongs here — company-approved free tools, or the same managed access with a smaller budget. This tier exists mainly to reduce shadow AI: people quietly using personal accounts because nothing sanctioned was available.
The part most frameworks skip
A tier list is not a policy on its own. What makes it work is the promotion loop: when someone in the base or middle tier repeatedly hits their allowance, that is a signal, not a problem to suppress. It triggers a review of the work, the value it is producing, and the economics — and a promotion to a higher tier if the case holds up.
This inverts the usual approval process. Instead of asking every employee to justify AI access in advance, you let real usage patterns surface who is getting value, and you invest there. Budget follows evidence, not job title.
Why this needs a control point
None of this is enforceable from a spreadsheet. It requires a control point that can see which team is using which model, at what volume, and route requests according to the tier someone is actually in. That is the same infrastructure question we cover in how we deliver AI governance — cost attribution and policy enforcement have to sit inside the request path, not in a document nobody reads after the kickoff meeting.
The pyramid is also where Secure Vibe picks up: once a workflow has proven itself with a champion or a team, it stops being a personal habit and becomes a case for software you actually own.